A copied cURL command is often the quickest description of a request that worked somewhere else. It is not automatically a request that a web page can reproduce. The shell, the cURL process and the browser have different responsibilities. Converting the command is useful, but the real task is identifying which parts describe the API operation and which parts belong to the original execution environment.
Reduce the command to a readable example
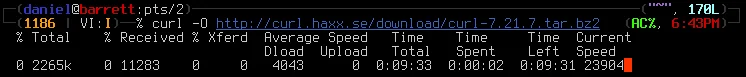
Begin with a synthetic request, not a copied authorization token. The following command describes a JSON body sent to an example address. The local converter produces code as text; it does not send the request, run the command or verify that the address implements an API.
curl 'https://example.com/api' -H 'Content-Type: application/json' -d '{"name":"Ada"}'
The expected Fetch options include POST, the JSON Content-Type header and the original body string. Read those three elements in the output before copying it. cURL's data options influence the method when no explicit method overrides it, so a converter that merely replaces the executable name would miss part of the request. This tool handles a restricted set of flags and rejects unsupported ones rather than inventing equivalent browser behavior.
Understand which parser handled the quotes
The quote marks around the URL and JSON are instructions to a shell-style tokenizer, not bytes that should appear around the transmitted body. That distinction becomes important when the body contains spaces, apostrophes or escaped double quotes. Compare the generated JavaScript string with the intended payload character by character when the example becomes more complicated.
Avoid treating the converter as a general shell interpreter. File references beginning with @, substitutions, redirection and unsupported flags are outside its scope. If an exported command contains those features, simplify a sanitized copy or write the Fetch call directly after understanding the original request. Do not delete flags merely to make an error disappear; a flag may represent behavior the browser cannot provide.
Account for the browser boundary
A command-line process can make a request that page JavaScript is not allowed to inspect. Cross-origin requests depend on the browser's CORS rules and the server's responses. Changing the JavaScript syntax does not grant permission. When a browser blocks a converted request, inspect its actual network evidence rather than assuming the payload must be malformed.
Setting no-cors is not a general solution for reading a blocked API response. It restricts the request and produces an opaque response whose body is unavailable to the page. Decide whether the API is intended for browser clients, whether a permitted same-origin route exists, or whether the integration belongs in a backend you control. Those are architecture and server-configuration decisions, not encoding tricks the converter can perform.
Remove assumptions about headers and identity
Some headers are managed or restricted by the browser. This converter rejects several such headers, including Cookie, Host and Content-Length, because reproducing their text in a Fetch options object would suggest control the page does not have. Read a rejection as a boundary to investigate. Do not assume another header spelling or capitalization bypasses browser policy.
Authentication deserves its own review. A successful request in a signed-in browser, a terminal with a token and a clean browser profile may represent three different identities. Check the API's documented credential mechanism and your application's authorized handling of it. Never place a private server credential into frontend code just because a copied cURL request used it. Generated code does not make that credential suitable for public distribution.
Check the response deliberately
Fetch gives you a response object even for ordinary HTTP error statuses. In application code, inspect the status or response.ok before treating the result as success. Also choose a body reader that matches what the API actually returns. The converter emits response.text() as a transparent starting point; replacing it with response.json() assumes the body is JSON and parsing can succeed.
Build a small test plan in your own authorized environment: the expected success status and body shape, a documented validation error, and a network failure or cancellation case. Keep test data synthetic where possible. These checks validate the integration rather than the converter alone. If the endpoint has side effects, use its approved test environment and avoid casually replaying a production write request while troubleshooting.
Keep the converted code reviewable
Before committing, replace incidental example values with explicit application inputs and remove copied debugging headers that are not needed. Keep method, headers and body easy to inspect. Record the browser-specific decisions separately from the command's original intent so another developer can explain why the final implementation is not a verbatim copy.
The finished result is a small, understood Fetch call with a documented response path and a clear credential boundary. The local tool saves typing and exposes supported translations. It cannot establish CORS permission, account authorization, endpoint behavior or a safe place to store secrets. Those checks remain part of integrating the API, even when the generated code looks complete.